33TS Intelligence Ltd. · London

Enterprise security you stay in control of.

33TS builds endpoint security and secure communications for organisations that cannot afford a breach — engineered by the incident responders who handle them.

Built for organisations where a breach is not an option

24/7
Senior incident response
30–60 s
dome: detection to action*
−80%
dome: mean time to respond*
2025
Founded in London
[Certifications and analyst recognition — placeholders until audited]

* Illustrative dome metrics. See methodology on dome.33ts.uk.

Platforms

Two platforms. One operating principle: you approve.

Flagship product

dome

Endpoints under control, access without VPN. AI investigates, you approve.

  • Inventory and patching
  • Detection and AI investigation
  • Zero trust access without VPN
  • Compliance and risk in money (FAIR/ROSI)
dome / security operationsIllustrative metrics
Exposure
15
critical patches
Threats
1
awaiting approval
Access
42
ZTNA sessions
● Verdict: MALICIOUS · 95% confidenceApprove
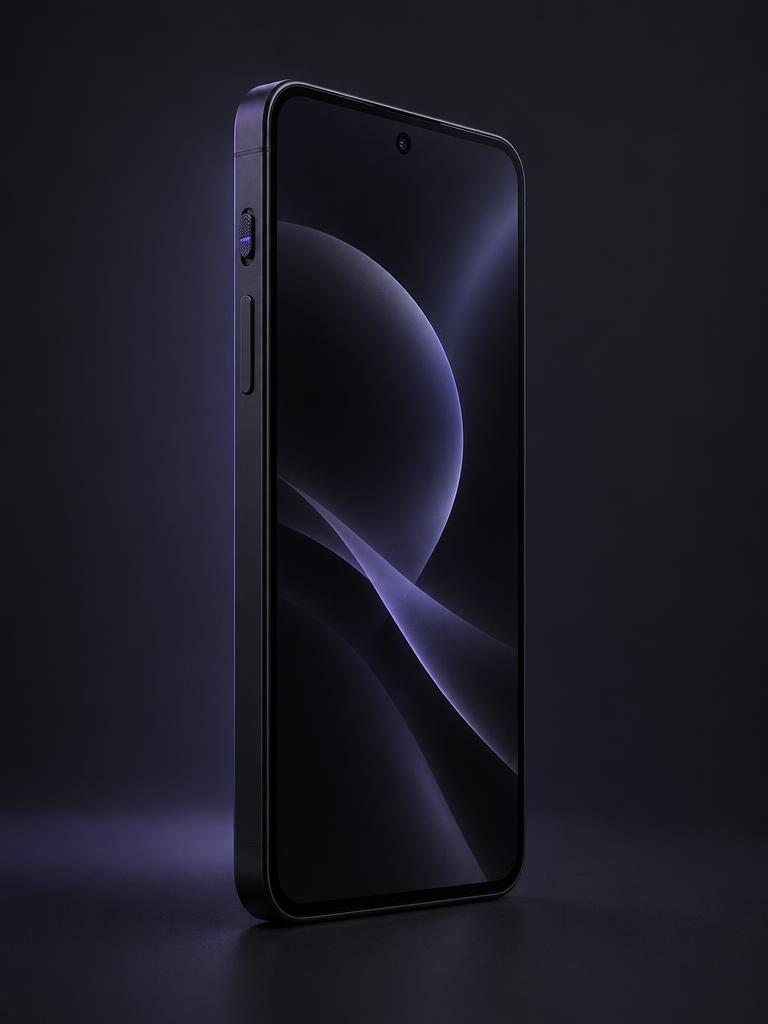
NyX secure phone
Secure mobile

NyX

The phone where not even the operator reads your messages.

  • Hardened GrapheneOS
  • ML-KEM-768 post-quantum encryption
  • Physical airgap
  • Zero-knowledge vault and blind server
Explore NyX
dome

Six capabilities. One single dashboard.

01

Visibility

Prioritise the flaws that matter: inventory, patches, EOL, Shadow IT and Shadow AI.

02

Detection

C2 beacons, DGA, credential theft and lateral movement.

03

Investigation

AI correlates signals and presents evidence before any action.

04

Remote access

Only the authorised resource, no VPN. Posture checked on every connection.

05

Compliance

Audit evidence and an immutable trail.

06

Strategy

Risk in money with FAIR / ROSI. The technical view, translated for decisions.

See dome
Services

Backed by senior incident responders

Incident response retainers, threat intelligence, digital forensics, advisory and dome MDR — delivered under strict confidentiality.

  • Incident response 24/7 and retainer
  • Threat intelligence
  • Digital forensics
  • Security advisory
  • dome MDR
View services

Experiencing a breach?

Senior incident responders. Confidential from the first message.

Under attack? IR 24/7
Typical engagements

Where we are typically called in

These are representative scenarios, not client case studies. We do not name clients or publish outcomes.

Professional services
When a firm suspects ransomware or an unauthorised intrusion, 33TS is called in to contain the incident, establish scope and support eradication and recovery. The work is senior-led and confidential from the first contact, with a report fit for the board and regulators.
Financial services
Security and intelligence teams need to know who is targeting their sector, executives or region. 33TS provides actor profiles, exposure monitoring and actionable briefings, and that intelligence informs detections in dome and the threat models used for NyX.
Boards and legal
During litigation, investigations or other sensitive matters, boards and legal teams need communications they control. 33TS supplies NyX — hardened devices with post-quantum encryption — so conversations do not depend on trusting the operator.
33TS

Why 33TS

Born in real incidents

What our team saw in attacks became detection in dome and a design requirement in NyX.

Human in command

In dome, AI recommends and you approve. In NyX, nobody but you holds the keys.

An expert one click away

Customers of both products can escalate to the 33TS senior incident response team.